4 min readGuide
Privacy, Secure Aggregation and Robustness in DFL
Combine differential privacy, secure aggregation and robust DFL with explicit trust assumptions, local threat budgets and joint evaluation.
Research notes and technical guides on federated learning, distributed AI, cyberdefense, trustworthy systems, and privacy-preserving platforms.
Topic: Trustworthy AI Clear topic
9 articles. Page 1 of 2.
4 min readGuide
Combine differential privacy, secure aggregation and robust DFL with explicit trust assumptions, local threat budgets and joint evaluation.
5 min readResearch note
Open questions in robust DFL: dynamic graphs, manipulated context, privacy, missing modalities and experiments to test the limits.
5 min readResearch note
Evaluate DFL robustness with F1, false rejection, overhead and recovery. Interpret Flighter and compare clean and attacked conditions.
5 min readGuide
Design a DFL system with topology, message contracts, mixing weights, recovery policies and per-client evaluation.
5 min readResearch note
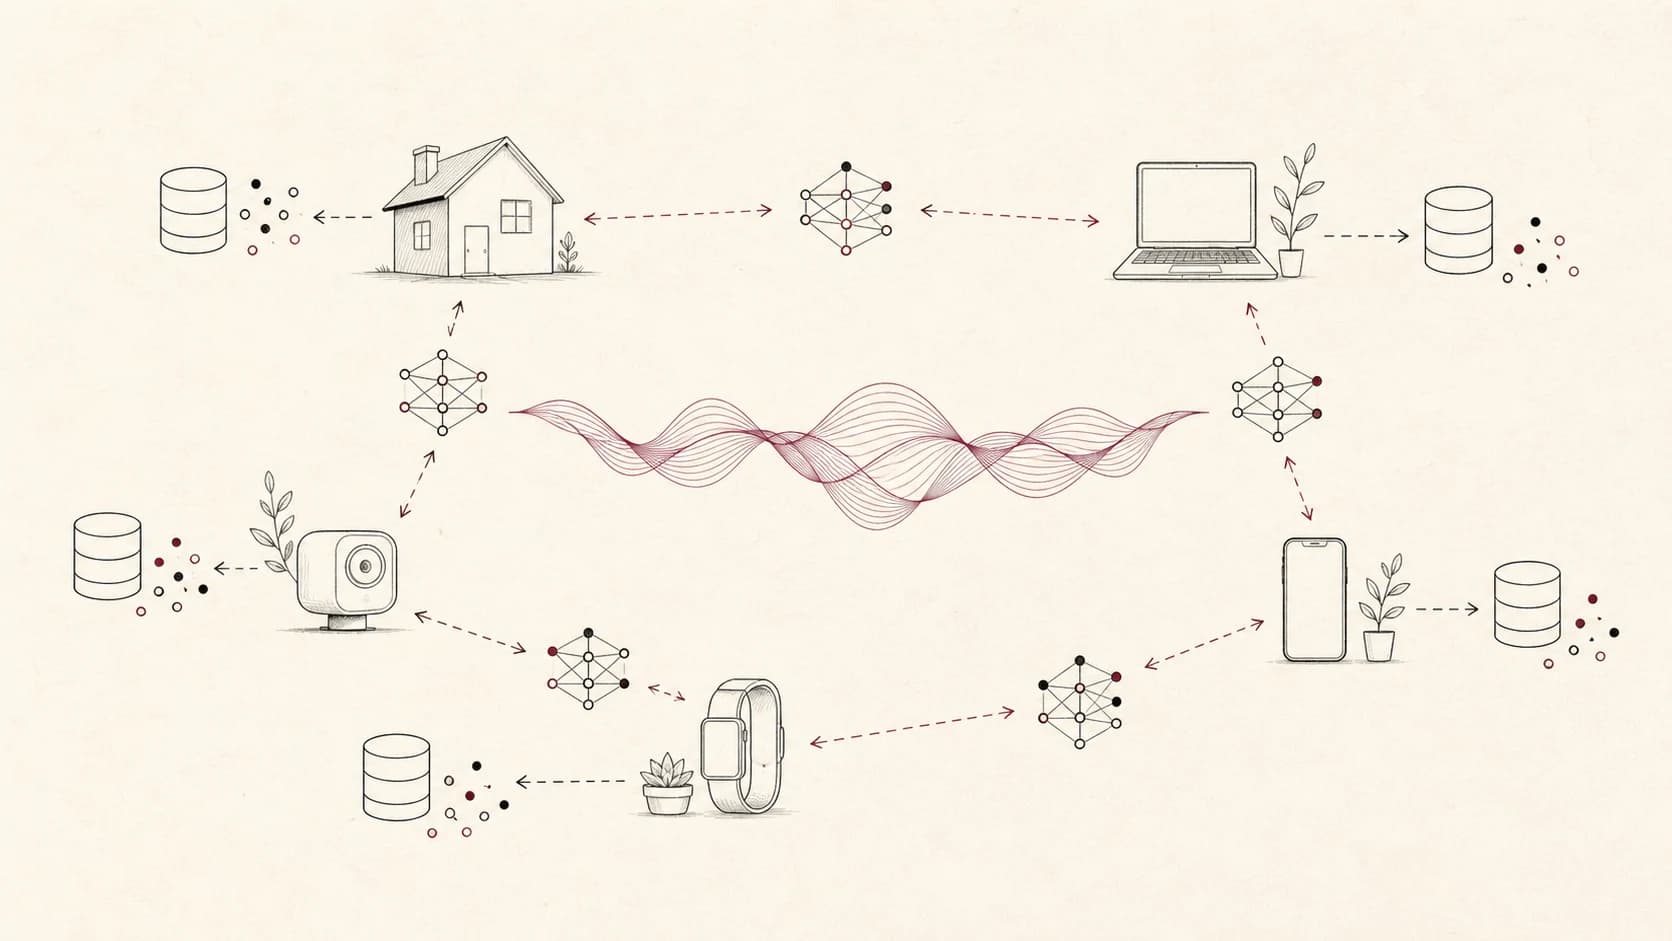
Why DFL changes coordination, consensus and trust. Identify central dependencies and test which services survive a failure.
5 min readResearch note
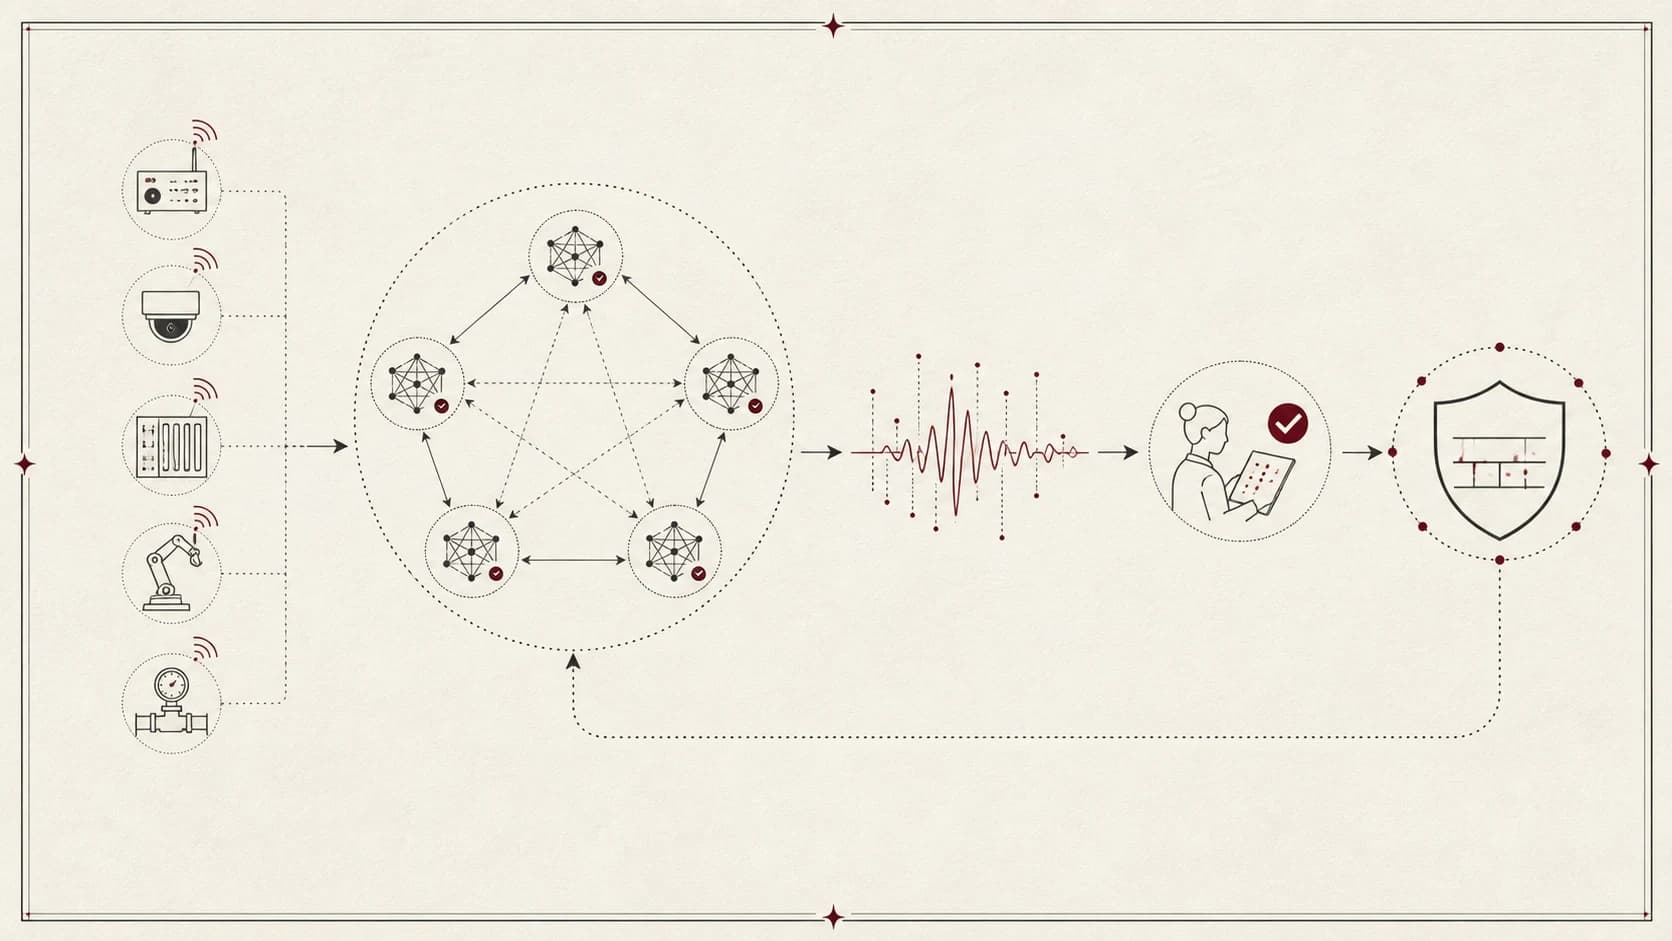
Connect telemetry, federated learning, alerts and LLM-assisted mitigation with traceable evidence, validation and reviewed feedback.
This site loads optional analytics from Google and external analytics providers only if you accept. You can decline and continue using the site normally.