4 min readGuide
Privacy, Secure Aggregation and Robustness in DFL
Combine differential privacy, secure aggregation and robust DFL with explicit trust assumptions, local threat budgets and joint evaluation.
Research notes and technical guides on federated learning, distributed AI, cyberdefense, trustworthy systems, and privacy-preserving platforms.
13 articles. Page 1 of 3.
4 min readGuide
Combine differential privacy, secure aggregation and robust DFL with explicit trust assumptions, local threat budgets and joint evaluation.
4 min readGuide
Evaluate prompt injection in RAG and LLM agents with paired tests, permission checks, tool traces and recent benchmark research.
4 min readGuide
LLMs for cybersecurity: SOC use cases, evidence, permissions and evaluation. Move from summarization to a tool-using assistant.
4 min readGuide
LLM-assisted mitigation: playbooks, evidence, permissions, idempotency and recovery. Turn recommendations into verifiable actions.
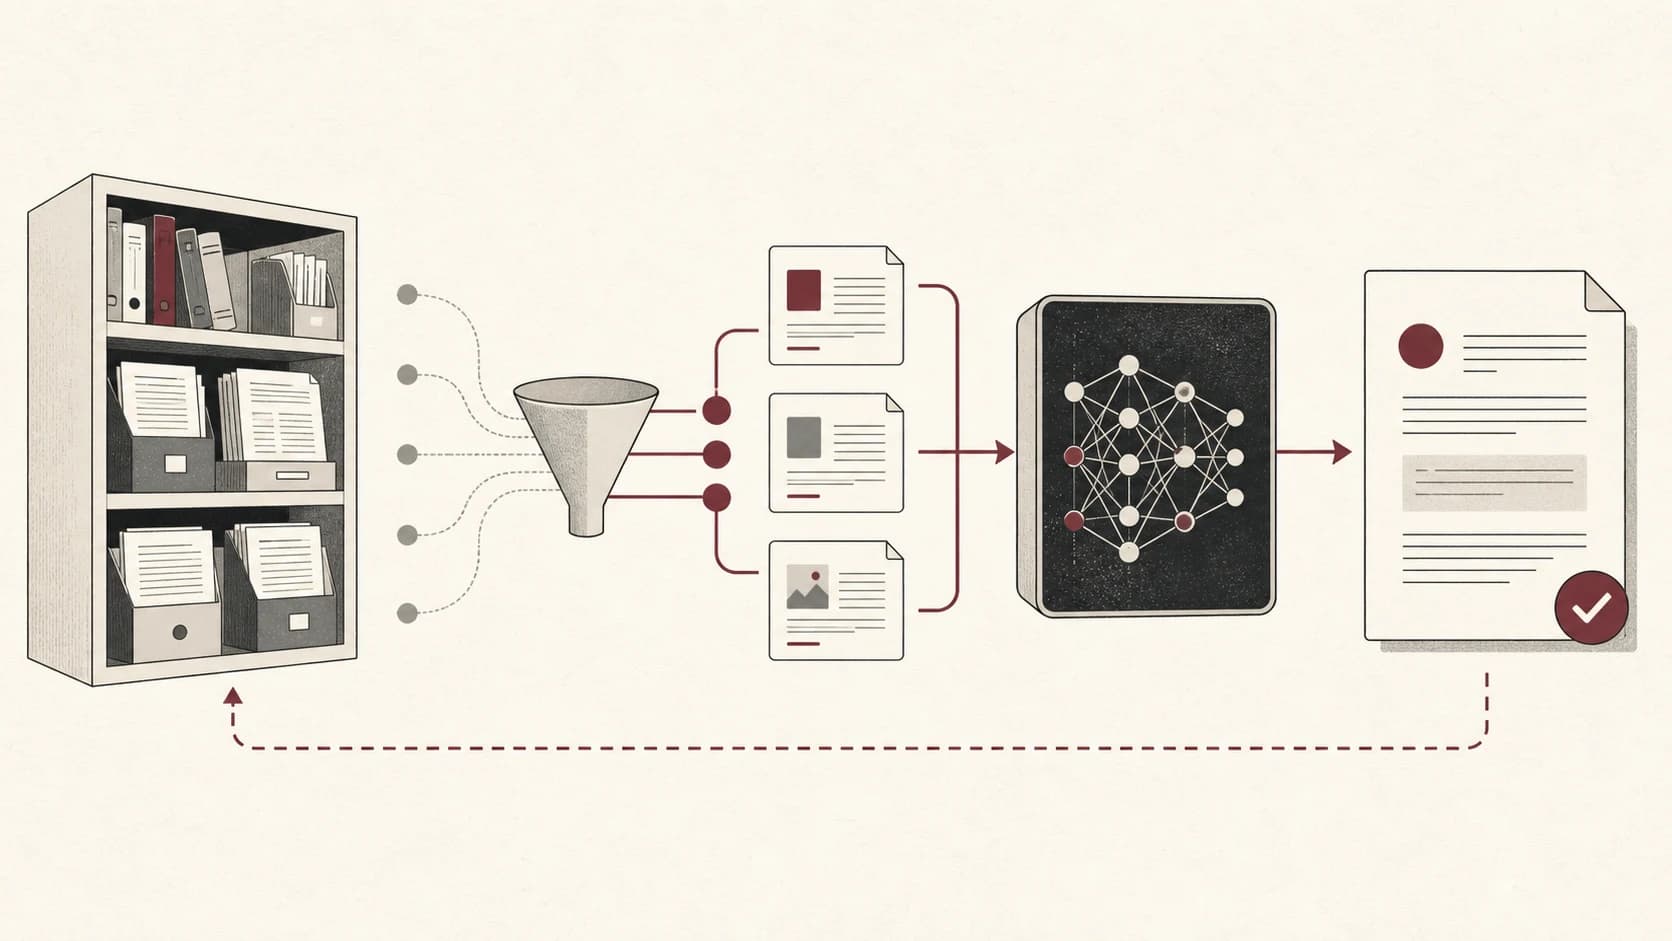
4 min readGuide
RAG for cybersecurity: hybrid retrieval, current sources, permissions and evaluation. Diagnose retrieval and generation failures.
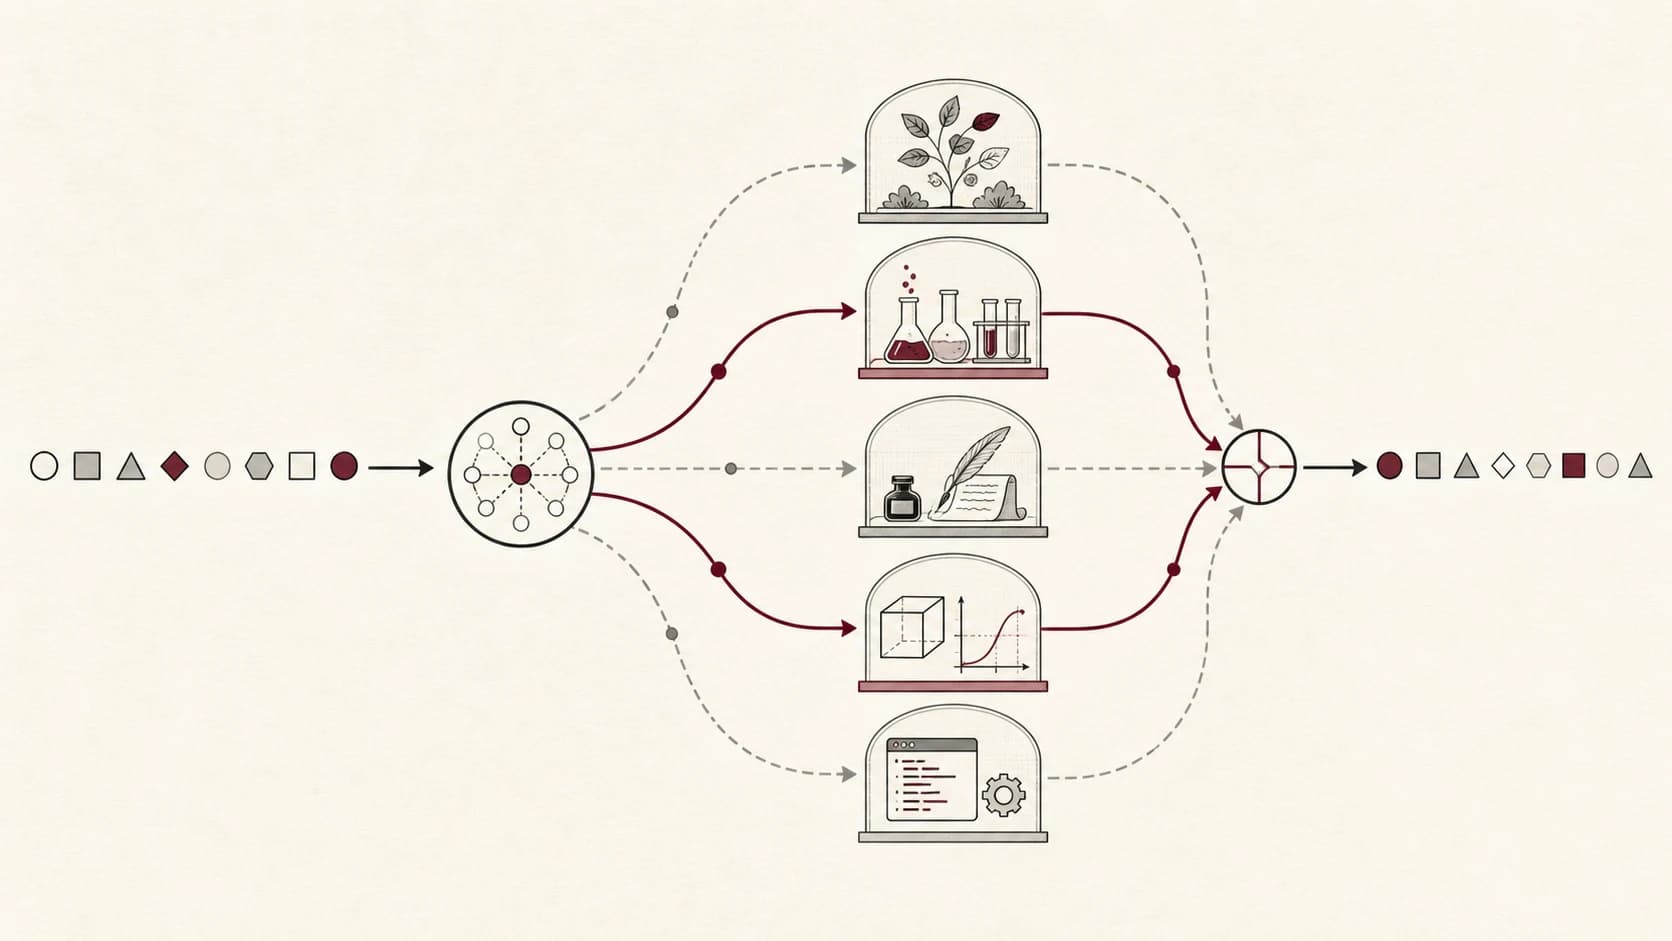
3 min readGuide
How MoE LLMs work: routing, active parameters, memory, load balance and latency and quality evaluation across languages.
This site loads optional analytics from Google and external analytics providers only if you accept. You can decline and continue using the site normally.