5 min readResearch note
Robust Decentralized Federated Learning: Limits and Open Questions
Open questions in robust DFL: dynamic graphs, manipulated context, privacy, missing modalities and experiments to test the limits.
Research notes and technical guides on federated learning, distributed AI, cyberdefense, trustworthy systems, and privacy-preserving platforms.
Topic: Trustworthy AI Clear topic
7 articles. Page 1 of 2.
5 min readResearch note
Open questions in robust DFL: dynamic graphs, manipulated context, privacy, missing modalities and experiments to test the limits.
4 min readResearch note
Autonomous cyberdefense with LLMs: control states, action boundaries, recovery and separate evaluation of utility and safety.
3 min readResearch note
P-RAG versus contextual RAG: parametric memory, updates, permissions and provenance for cybersecurity knowledge.
5 min readResearch note
Evaluate DFL robustness with F1, false rejection, overhead and recovery. Interpret Flighter and compare clean and attacked conditions.
5 min readResearch note
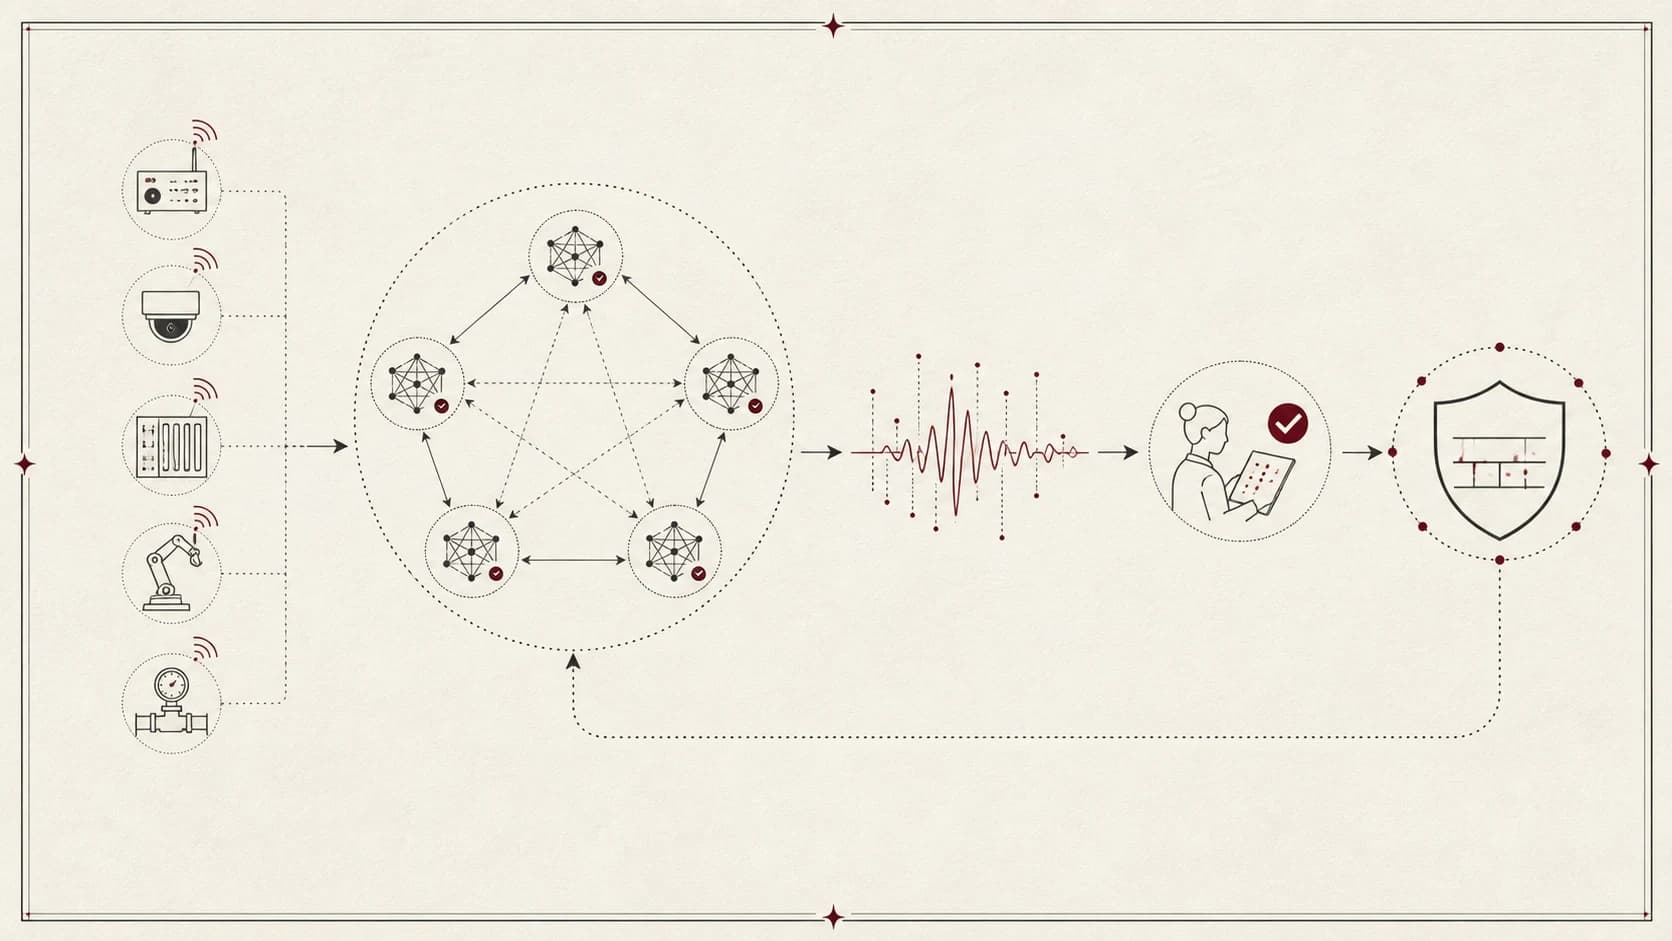
Connect telemetry, federated learning, alerts and LLM-assisted mitigation with traceable evidence, validation and reviewed feedback.
3 min readResearch note
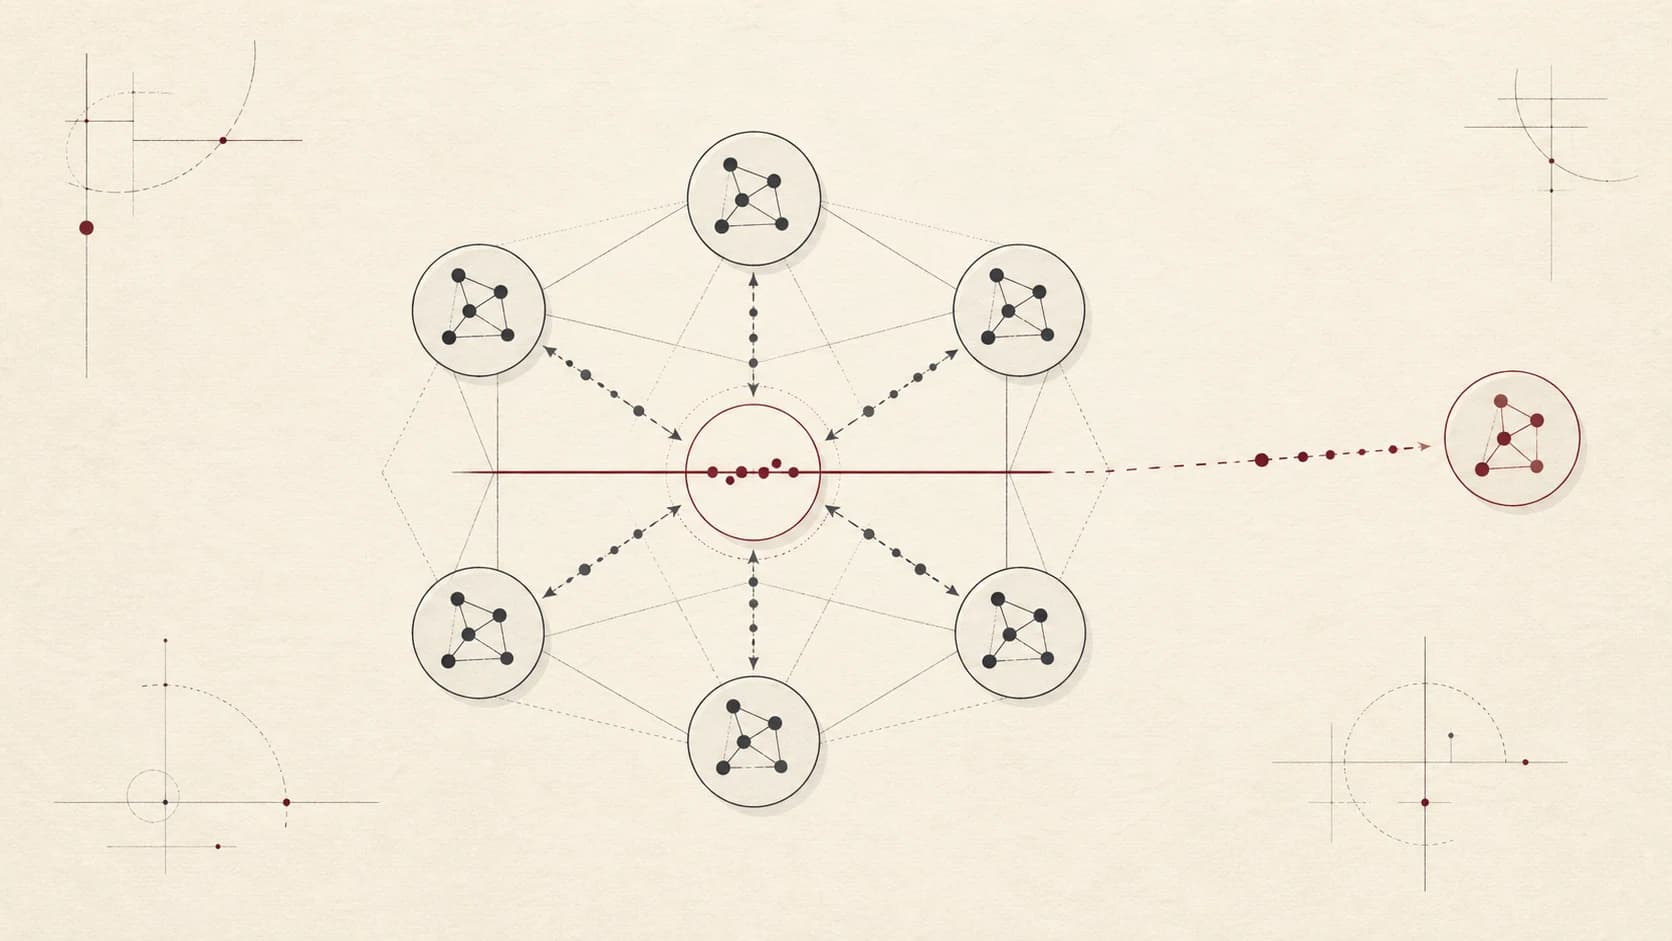
Median, trimmed mean and trust in DFL: examples, local poisoning assumptions and defense costs with legitimate non-IID clients.
This site loads optional analytics from Google and external analytics providers only if you accept. You can decline and continue using the site normally.