5 min readResearch note
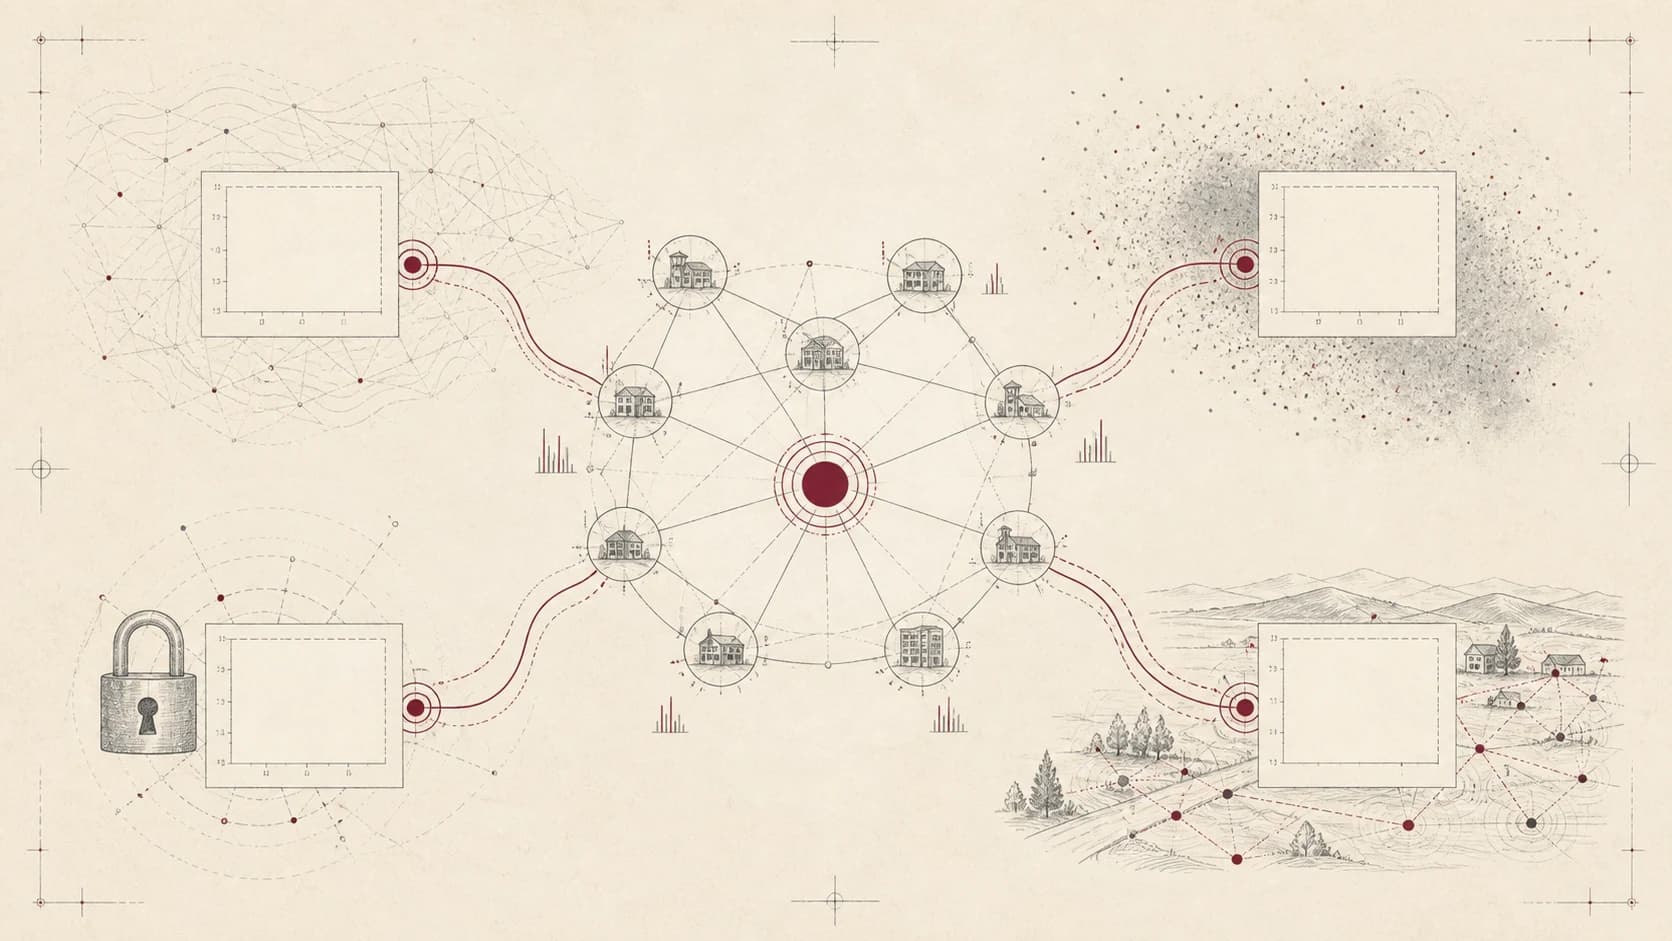
Robust Decentralized Federated Learning: Limits and Open Questions
Open questions in robust DFL: dynamic graphs, manipulated context, privacy, missing modalities and experiments to test the limits.
Research notes and technical guides on federated learning, distributed AI, cyberdefense, trustworthy systems, and privacy-preserving platforms.
Topic: Trustworthy AI Clear topic
9 articles. Page 1 of 2.
5 min readResearch note
Open questions in robust DFL: dynamic graphs, manipulated context, privacy, missing modalities and experiments to test the limits.
4 min readGuide
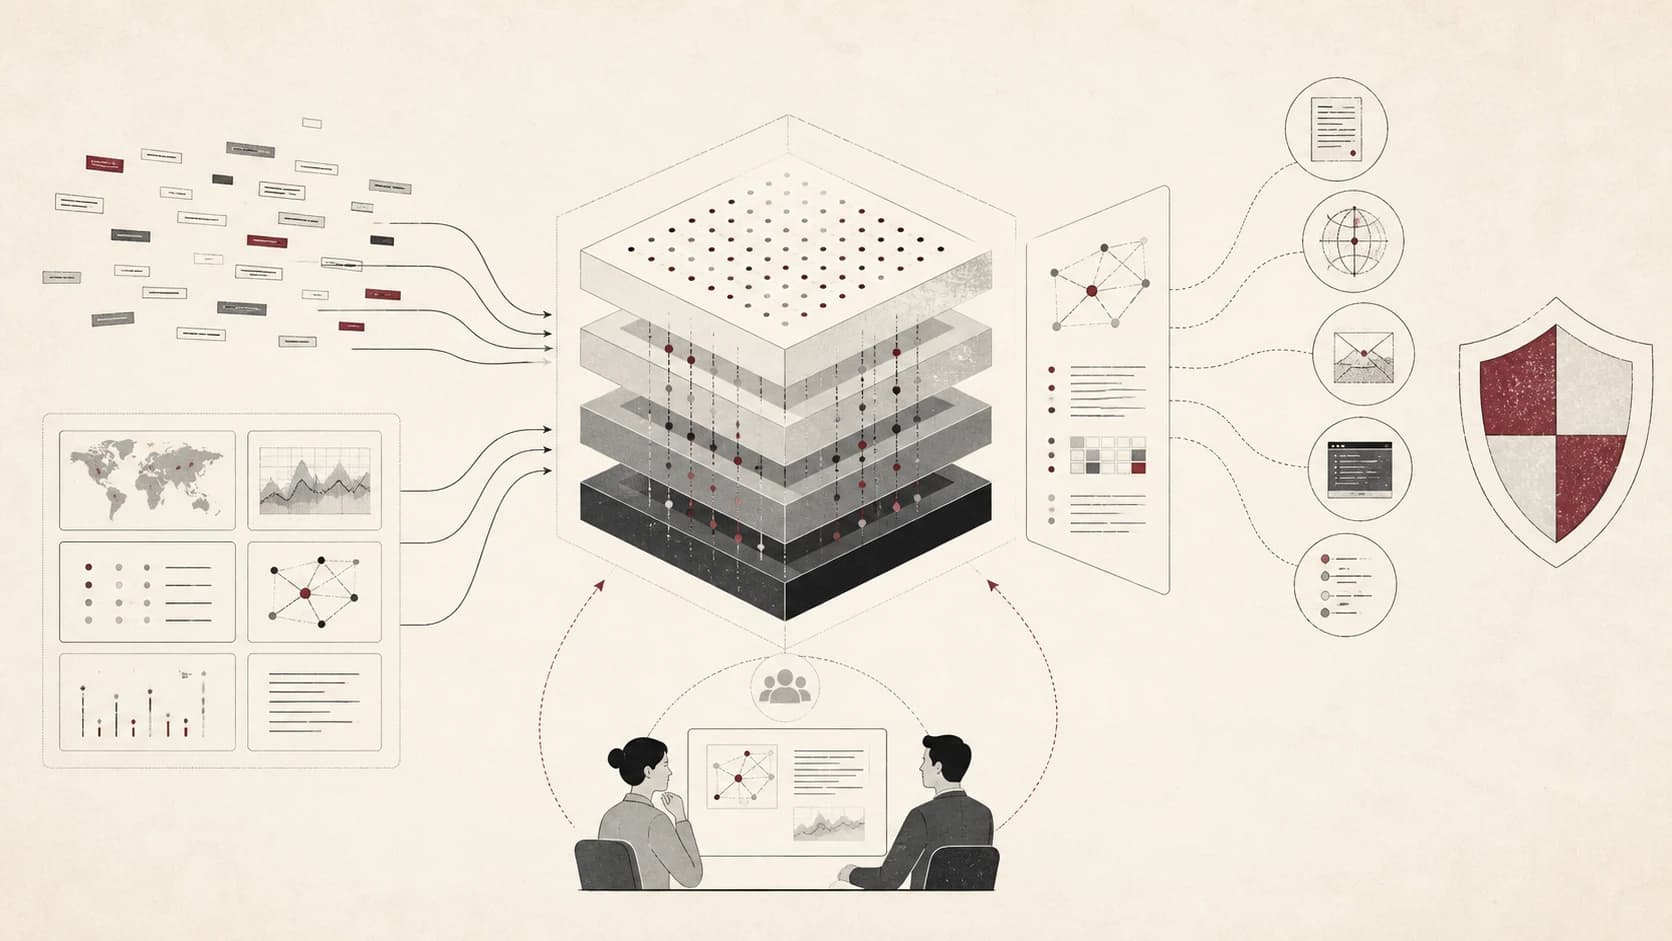
LLMs for cybersecurity: SOC use cases, evidence, permissions and evaluation. Move from summarization to a tool-using assistant.
3 min readResearch note
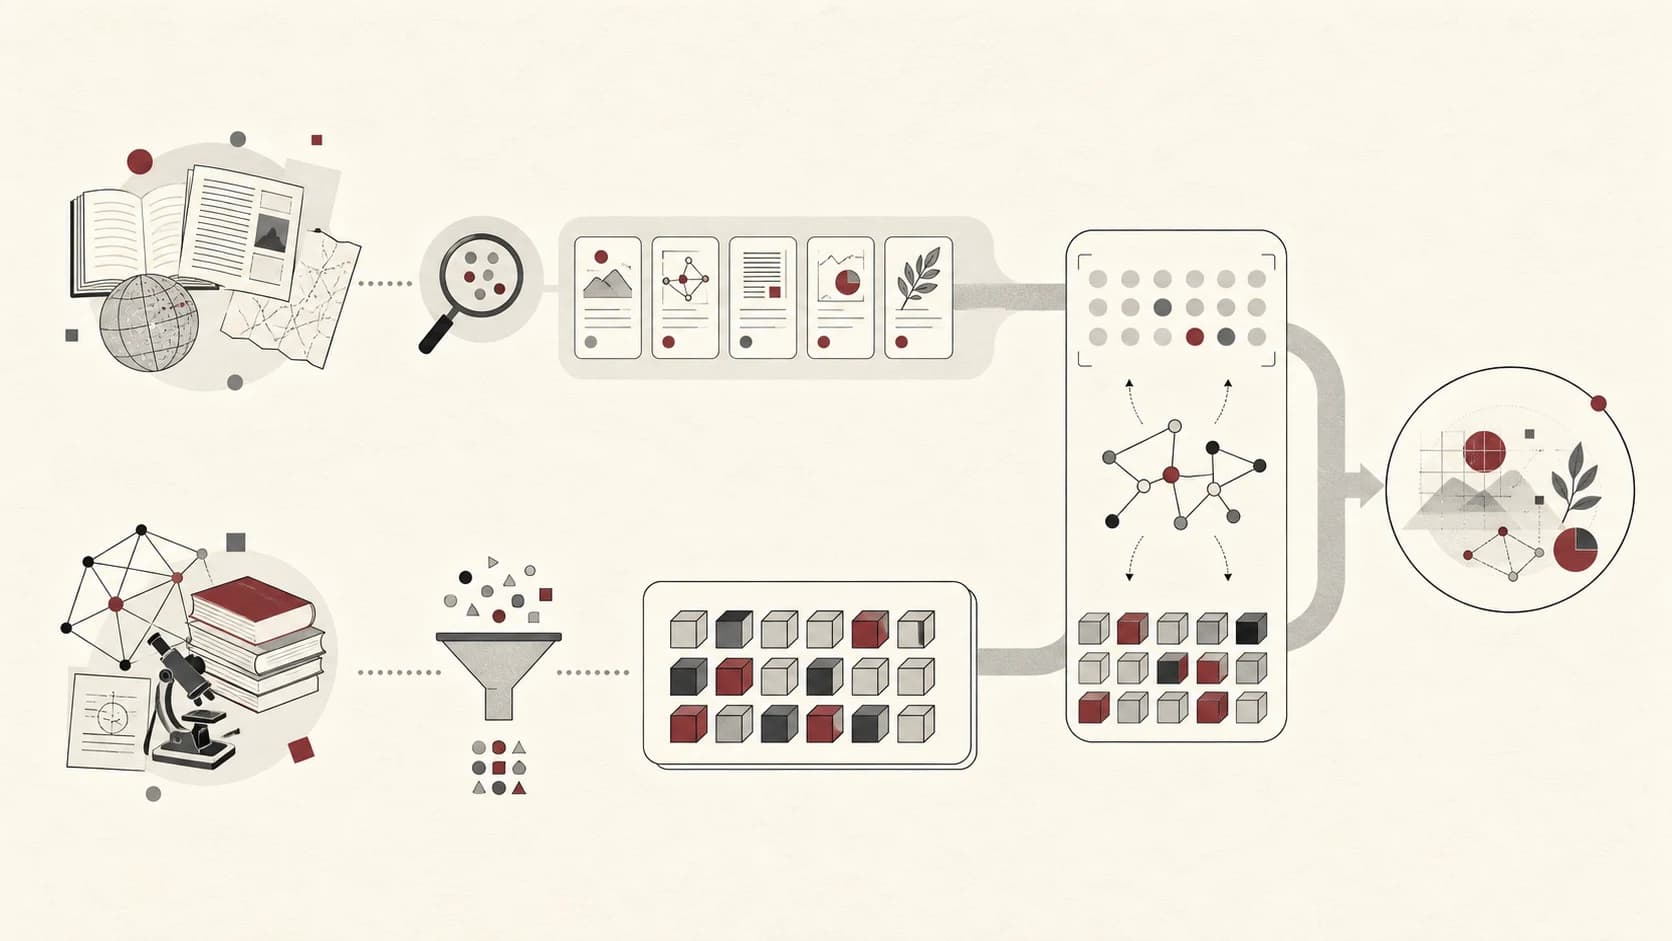
P-RAG versus contextual RAG: parametric memory, updates, permissions and provenance for cybersecurity knowledge.
3 min readGuide
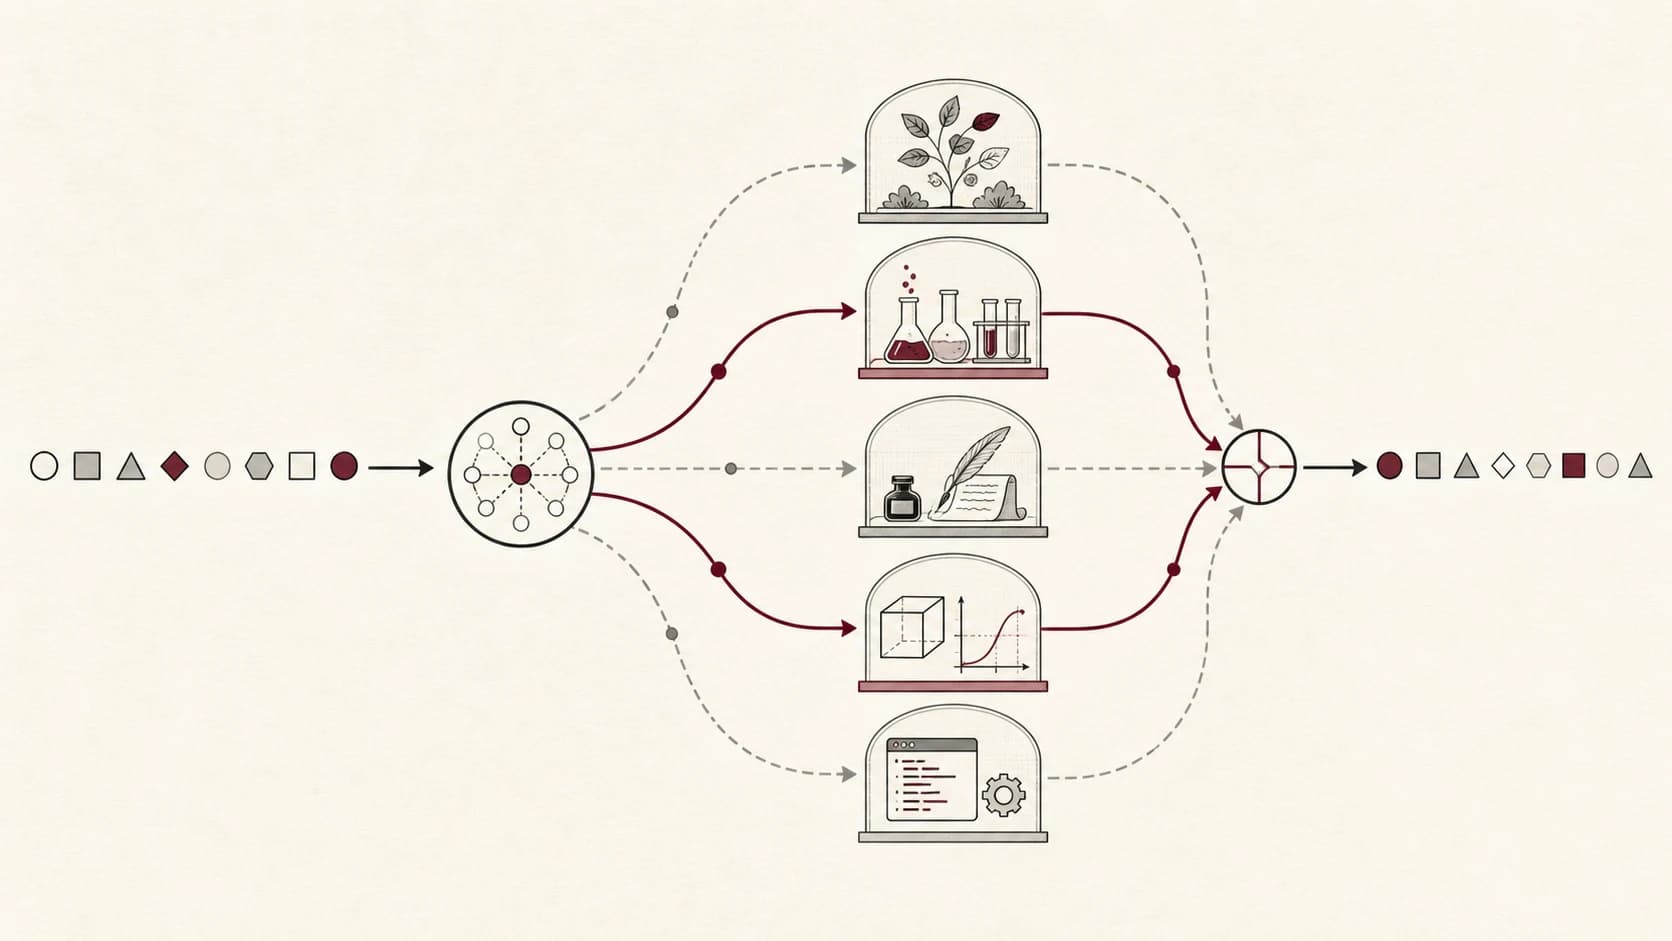
How MoE LLMs work: routing, active parameters, memory, load balance and latency and quality evaluation across languages.
3 min readGuide
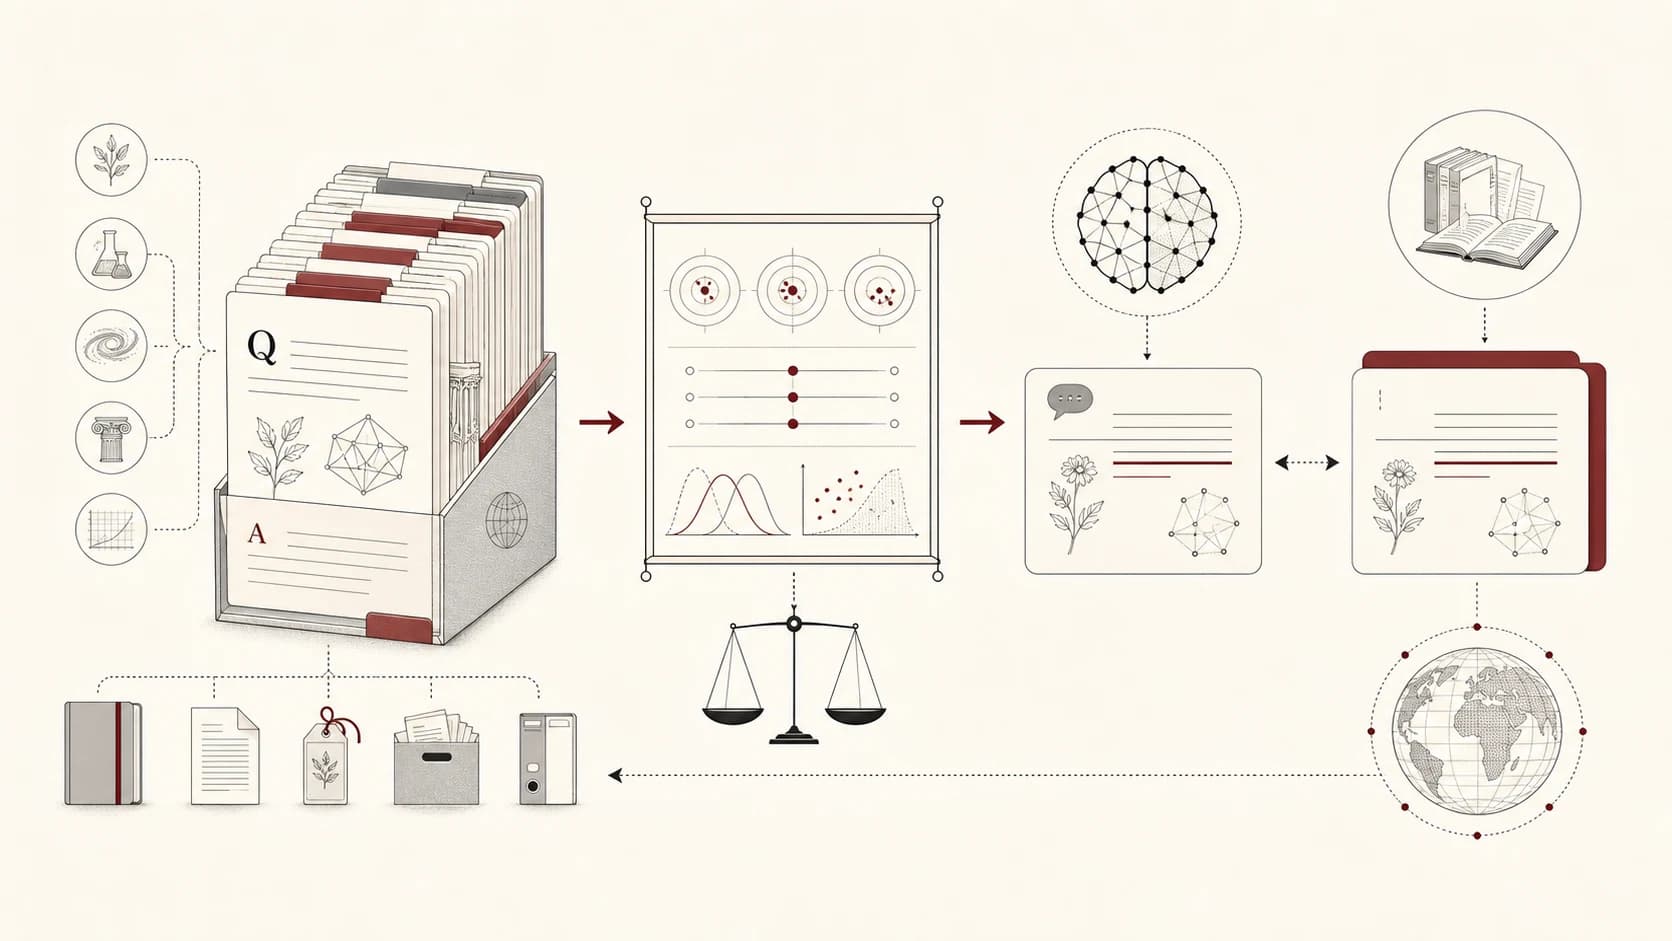
Build golden sets for LLMs and RAG with examples, adjudication, leakage-aware splits and bilingual security cases.
3 min readGuide
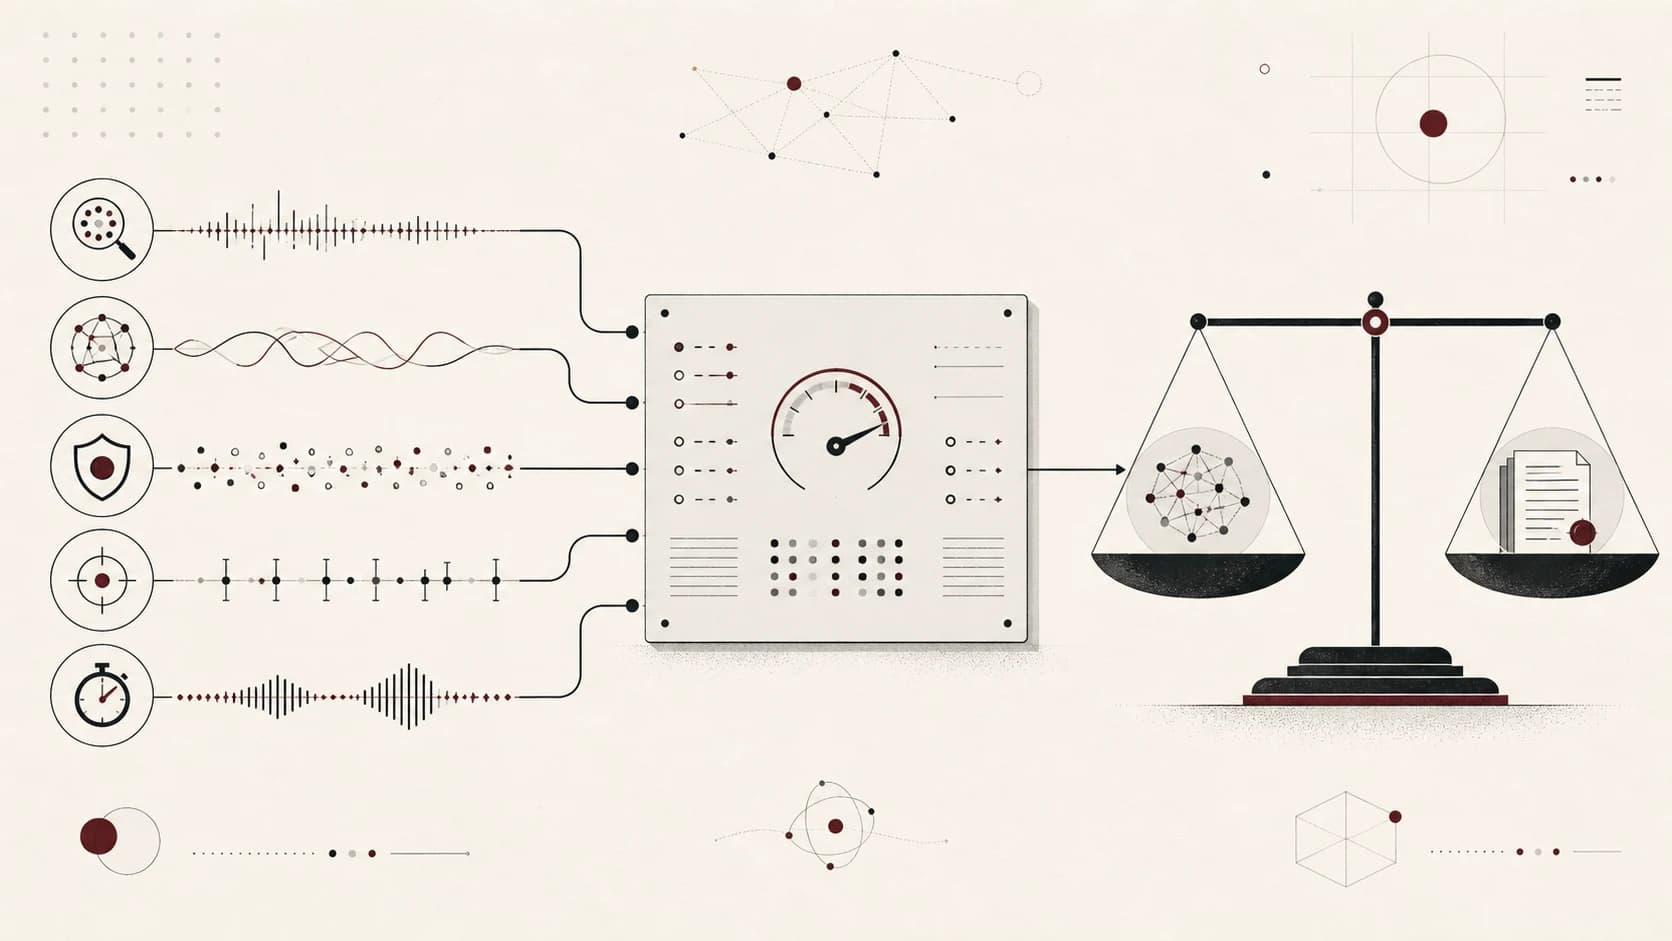
LLM and RAG metrics: retrieval recall, citations, unsafe actions, calibration, latency and uncertainty. Define fair comparisons.
This site loads optional analytics from Google and external analytics providers only if you accept. You can decline and continue using the site normally.